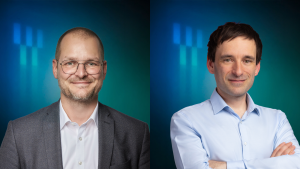
Cyberattacks cannot be prevented entirely. What matters is whether companies can remain operational when an incident occurs. Benjamin Tiggemann, Head of the IT Security Competence Team, and Dominik Kremers, Head of Business Customers at NetCologne Business, explain why cyber resilience requires more than technical security measures and the role that resilient IT infrastructure, clear responsibilities and thorough preparation play.
Find out more about “Cyber Resilience Beyond Theory” through expert presentations and panel discussions at the Internet Security Days on Tour on 19 November in Cologne. Register now!
1. Today, cyber resilience means more than preventing attacks wherever possible. In your view, what distinguishes a well-protected company from one that is genuinely resilient?
Benjamin Tiggemann: A well-protected company uses established security measures such as XDR, phishing-resistant MFA, robust identity and access management, and zero-trust principles. It understands its attack surface, monitors it continuously and provides regular staff training. Sufficient internal resources are also essential to manage security solutions and service providers effectively.
A resilient company goes one step further: it assumes that security incidents can occur despite all the measures in place. That is why incident response, backup and business continuity processes are regularly tested and improved. Backups are immutable and isolated from the production network.
The difference is that good security reduces the likelihood of an attack, while resilience limits its impact.
2. At the ISD Roadshow in Cologne, you will be discussing why cyber resilience begins in the data centre. What role do factors such as redundancy, backups and data sovereignty play, and where do companies underestimate their dependence on the underlying infrastructure?
Dominik Kremers: Many companies wonder whether their own server room or a hyperscaler is more secure. Hyperscalers have enormous resources and specialised security teams, but they also create dependencies in terms of data sovereignty and vendor lock-in.
From our perspective, the solution often lies in hybrid approaches. Companies that can flexibly move their infrastructure between different locations or providers significantly increase their resilience. Distributed data centres are particularly suitable for backups or as disaster recovery sites.
Furthermore, the effort required to operate secure infrastructure in-house is often underestimated. Local hosting providers frequently offer advantages in terms of transparency, data location and digital sovereignty.
3. With NIS2 and the requirements for critical infrastructure, regulatory pressure is also increasing. Are you seeing companies take a fundamentally more strategic approach to IT security as a result, or is there a risk that they will primarily focus on meeting new compliance obligations?
Benjamin Tiggemann: NIS2 introduces clear requirements and responsibilities extending all the way to senior management for the first time. This is an important step forward.
Nevertheless, we will see both developments: companies with established security processes can usually integrate the requirements without difficulty. Others focus primarily on formally fulfilling their compliance obligations.
The decisive factor will be how consistently the requirements are monitored and enforced. Only then will it become clear whether NIS2 leads to greater cyber resilience or is primarily regarded as a box-ticking exercise.
4. AI is changing both sides of cybersecurity: attackers can automate attacks more extensively, while new opportunities for defence are emerging. Is AI shifting the balance between attackers and defenders? And what does this mean in practical terms for companies that have neither unlimited budgets nor large security teams?
Benjamin Tiggemann: AI strengthens both attackers and defenders. Cybercriminals can personalise phishing campaigns and scale attacks more efficiently. At the same time, AI helps security teams detect anomalies more quickly and prioritise incidents more effectively.
AI presents an opportunity, particularly for companies with limited resources. They do not need to develop modern security solutions themselves but can rely on professional services and platforms with integrated AI capabilities. Nevertheless, the technology remains just a tool. Clear processes, responsibilities and a well-thought-out security strategy remain essential.
5. At the ISD Roadshow, you will be discussing cyber resilience with representatives from business, the public sector and the German Federal Office for Information Security (BSI). What questions should decision-makers urgently be asking themselves that are still too rarely raised in everyday discussions about security?
Benjamin Tiggemann: Our penetration tests highlight two key questions.
The first is: Do we really know our digital attack surface? We frequently discover forgotten systems, open access points or outdated applications that have neither been documented nor assessed. These significantly increase the risk.
The second is: What exactly is our IT service provider doing to secure our environment? As almost every company relies on external partners, their security measures should be reviewed regularly. Responsibility can be delegated, but liability cannot.
Both questions lead to the same conclusion: resilience begins with a realistic assessment of the actual state of a company’s IT.
6. Cyber resilience is often regarded as a technical issue. Why do you believe it is, above all, a matter of management and organisational culture today?
Dominik Kremers: Cyber resilience cannot be achieved through technology alone. Even the best security solutions are insufficient if responsibilities are unclear or companies only address risks after an incident has occurred. Resilient organisations address cyber risks at management level and integrate them into their risk management processes. Decisions about investment, emergency preparedness and data storage are made with business continuity in mind.
At the same time, cyber resilience is a matter of organisational culture. Employees must understand their roles, be able to act in an emergency and have clear processes to follow. Regular exercises and defined communication channels are just as important as technical security measures. Ultimately, resilience is not measured by whether an attack occurs, but by how quickly and effectively a company can respond to it in a controlled manner.
In summary, cyber resilience results from the interplay of technology, infrastructure, processes and a corporate culture that recognises security as a strategic responsibility. The key is not only to defend against attacks but also to maintain business operations during a crisis and restore them quickly.