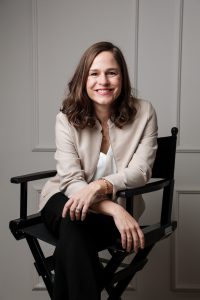
Effectively combatting DNS abuse is a collective effort. However, registrars, hosting providers and platforms have different responsibilities and scope for action. In the run-up to the eco Internet Security Days @ it-sa, we speak to Ashley La Bolle, Vice President of Domains at Tucows, about what is needed to respond more quickly to abuse, why meaningful reports are crucial and what role AI could play in the future.
1. Phishing, malware and other cyberattacks often exploit legitimate Internet infrastructure. What responsibilities do the various stakeholders in the Internet ecosystem bear when dealing with DNS abuse?
Every stakeholder in the Internet ecosystem has a responsibility to its customers and, within the scope of its infrastructure, to maintain a clean Domain Name System. DNS abuse not only directly harms victims, but also the entire infrastructure used for the attack.
At registrar level, for example, accounts used to purchase fraudulent domains are often flagged and domains blocked before an incident is even reported. This behind-the-scenes measure is one of the most effective ways of curbing DNS abuse. Registrars recognise that it is in their own interests to ensure that their Domain Name System does not attract attackers, both to protect their customers and their own systems.
At the same time, the various stakeholders in the Internet ecosystem have different spheres of influence and tools for responding to abuse. This is why Tucows, together with other ICANN-accredited registrars, has advocated uniform industry standards for combatting DNS abuse. These new obligations define which aspects of DNS abuse fall within a registrar’s remit and which lie outside it. This enables us to hold users accountable without causing collateral damage by intervening in cases where the measures available to us are limited and too drastic.
Registrars are just one part of a wider ecosystem: it is not only domain registrars such as Tucows that are responsible for preventing and curbing DNS abuse. Hosting providers should also take action against harmful content on their platforms, while social media providers should address abusive posts on their services. What manifests as DNS abuse can often originate elsewhere, for example in social media accounts that direct unsuspecting users to fraudulent websites, or in smishing attacks that distribute malicious links.
Every stakeholder in the ecosystem must take action in the areas where they can most effectively help to prevent abuse and mitigate its consequences.
Combatting DNS abuse is therefore important, but it is only one part of a larger whole. We repeatedly emphasise that neutral service providers must also remain neutral. Domain registrars should, of course, take consistent action against DNS abuse, but without moving into the area of content control.
2. At the Internet Security Days @ it-sa, you will discuss how the detection of DNS abuse can be translated into effective action more quickly. What are the biggest challenges along the way today?
One of the biggest challenges we see is the conflation of DNS abuse with complaints about content. As a result, we as a registrar receive many reports on which we cannot take action because they fall outside our remit. Given the harm caused by DNS abuse, our aim is to tackle it quickly. If our teams first have to sift through a large number of such complaints, this inevitably slows down our response to actual DNS abuse.
Since there is little money to be made from detecting and reporting DNS abuse, many of these reports come, for example, from brand protection companies whose priority is combatting trademark infringements. In some cases, these two processes are clearly separated, and we receive both actionable reports of DNS abuse and trademark-related complaints through our standard abuse reporting channel. That is excellent, and we greatly appreciate it. Others, however, conflate the two and submit DNS abuse “reports” without providing evidence that such activity has taken place.
We also see this as an opportunity to educate users and encourage them to provide meaningful evidence and substantiate their complaints. The better reporters understand what information is required and how different types of abuse should be categorised, the more precisely they can report cases. By ensuring that less time-critical reports are submitted through the appropriate channels, we can relieve pressure on the “emergency hotlines” and act much more quickly in critical cases.
Meaningful evidence is also crucial, as is educating reporters about the need to include it. Screenshots, logs, or a clear explanation and description of the DNS abuse in the report enable us to review reports and take action quickly – even if certain content is not immediately visible to our teams, for example due to geoblocking.
There are also efforts to develop and introduce a technical standard for reporting DNS abuse; unfortunately, the current standards for including evidence are not yet sufficient. Further action is still needed in this area.
3. Bei der Bekämpfung von Missbrauch muss schnell, aber auf belastbarer Grundlage gehandelt werden. Wie lässt sich dieses Spannungsfeld aus Ihrer Sicht auflösen?
When combatting abuse, action needs to be taken quickly, but on a robust basis. How can this tension be resolved in your view?
Infrastructure providers generally publish guidance on the types of evidence they require in different cases and how reporters can best transfer it. This can be frustrating, as there appears to be no standardised approach. However, broadly similar standards have become established within the respective sectors: registrars generally require comparable evidence, as do hosting providers. While the requirements of registrars and hosting providers may differ from one another, they are often similar within each respective sector.
It is therefore crucial to understand the requirements of the relevant recipient and provide the necessary information from the outset. This allows reports to be reviewed more quickly and action to be taken sooner.
4. Looking ahead to the discussion at it-sa, which aspect of DNS abuse and cyber resilience should security professionals be paying more attention to?
As in almost every other field these days, there is lively debate within the security and cyber-resilience community about how large language models (LLMs) could exacerbate DNS abuse. However, as with any tool, the outcome depends on how it is used. LLMs can help infrastructure providers efficiently identify patterns of fraud and rapidly prioritise reports, enabling providers to monitor their platforms more effectively and identify activities that might otherwise have gone unnoticed. There is a genuine opportunity to enhance security measures with the help of LLMs, provided they are deployed thoughtfully.
Find out more at the Internet Security Days @ it-sa: On 28 October 2026, Ashley La Bolle will join other experts to discuss how cyber resilience against DNS abuse can be strengthened and how the path from detection to effective response can be improved. Further information on the programme and registration is available on the Internet Security Days @ it-sa event page.